This article describes how security roles function within an Infinite Campus-only environment.
The following diagram illustrates the user's ability to create and delegate Product Security roles.
There is a distinct difference between single and multi-product environments. The following diagram illustrates the process for users with Campus SIS only.
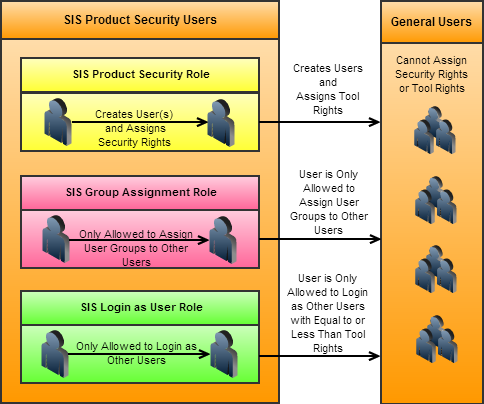
You may choose to have a single Product Security user or multiple Product Security users. If you have questions about which configuration is right for you or about best practices, please contact Infinite Campus.
Product Security Role Assignments
Product Security Roles determine whether a user may assign Tool Rights to other Campus Application users. Product Security Roles are assigned to users on each person's User Account. The Product Security Role Assignments section displays when Campus Application is selected in the Homepage dropdown list. Users assigned the Product Security Role automatically inherit all tool rights associated with the specific product.
Campus automatically assigns users with a Product Security Role calendar rights of All Calendars/All Schools with Data Modification Rights regardless of calendar rights assigned in their user account.
Users with a Student Information System Product Security role are allowed to log in as a user with a Student Information System - Login as User Product Security Role, but once they have logged in as that user, they cannot use that user account to then log into another Campus user account via the Login as User button on the User Account.
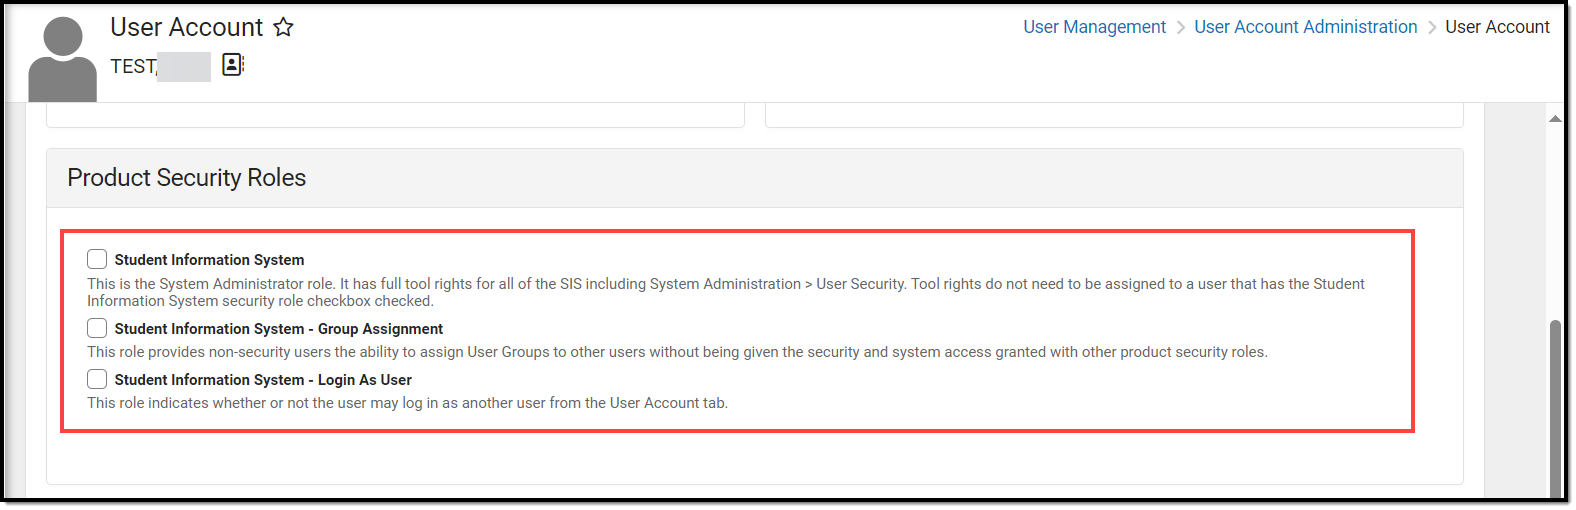
Student Information System Product Security Role
The Student Information System product security role grants administrative rights to ALL non-finance tools within Infinite Campus. This role should only be given to system administrators within the district.
This role does not grant a person rights to Human Resources, Finance, Payroll, or Staff Evaluation tools. These tools must be granted via their respective product security roles or tool rights.
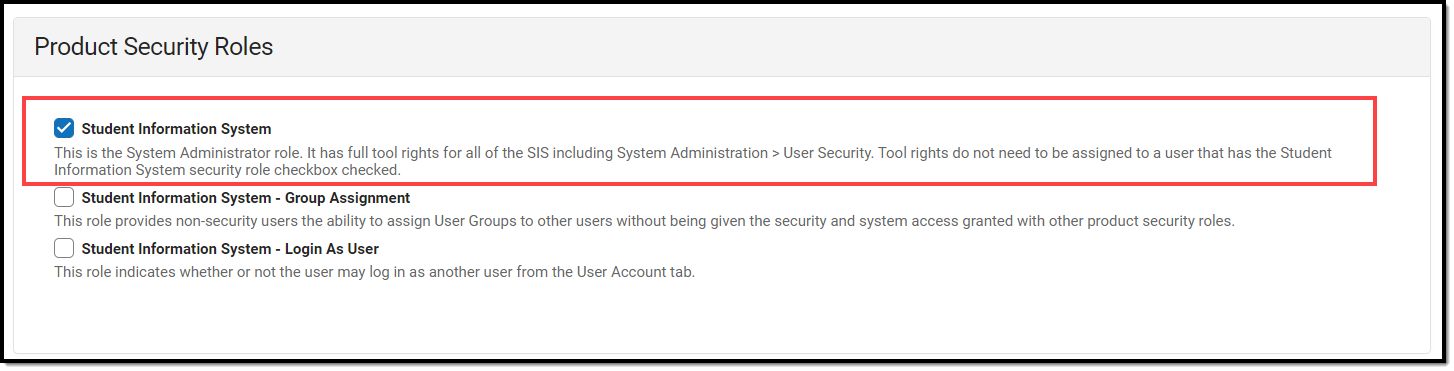
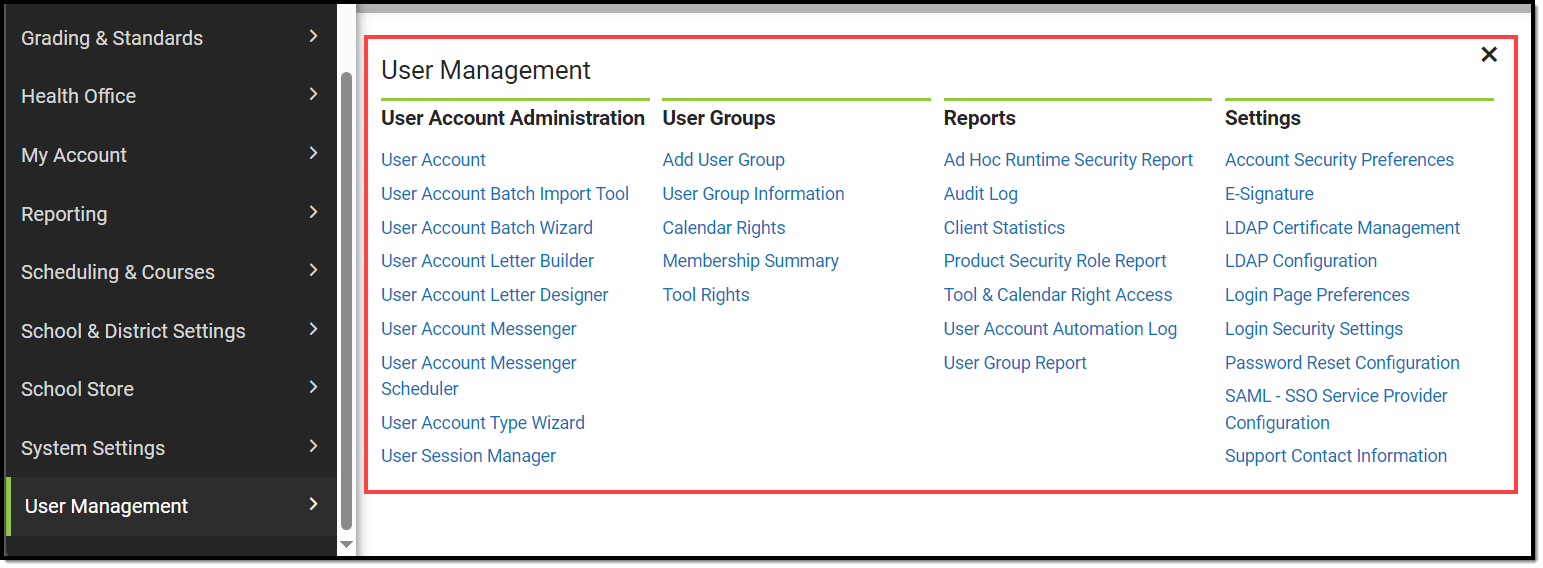
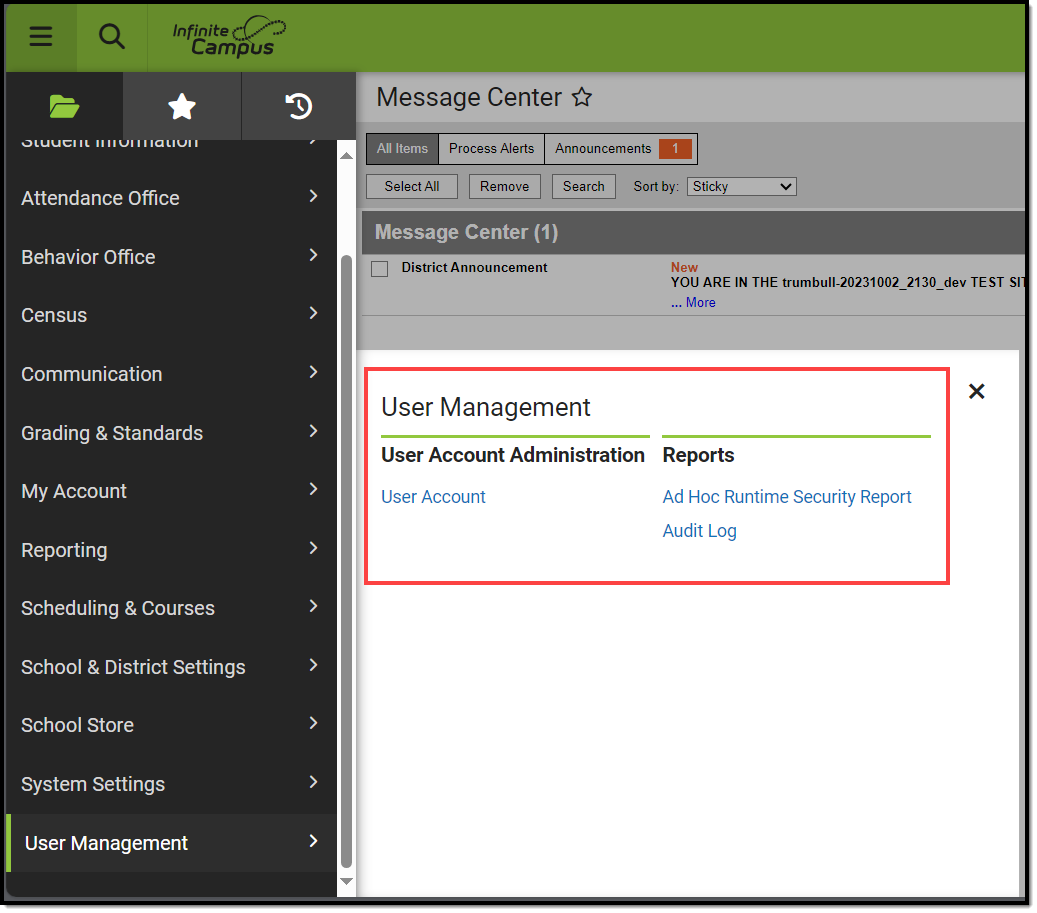
Users MUST be assigned the Student Information System product security role to create User Groups and access most User Management features. The table below shows how access to User Management tools differs between the SIS product security role and a user with only tool rights.
SIS Product Security Role |
 |
User with All Tool Rights (but no SIS Product Security Role) |
 |
Login As User Feature
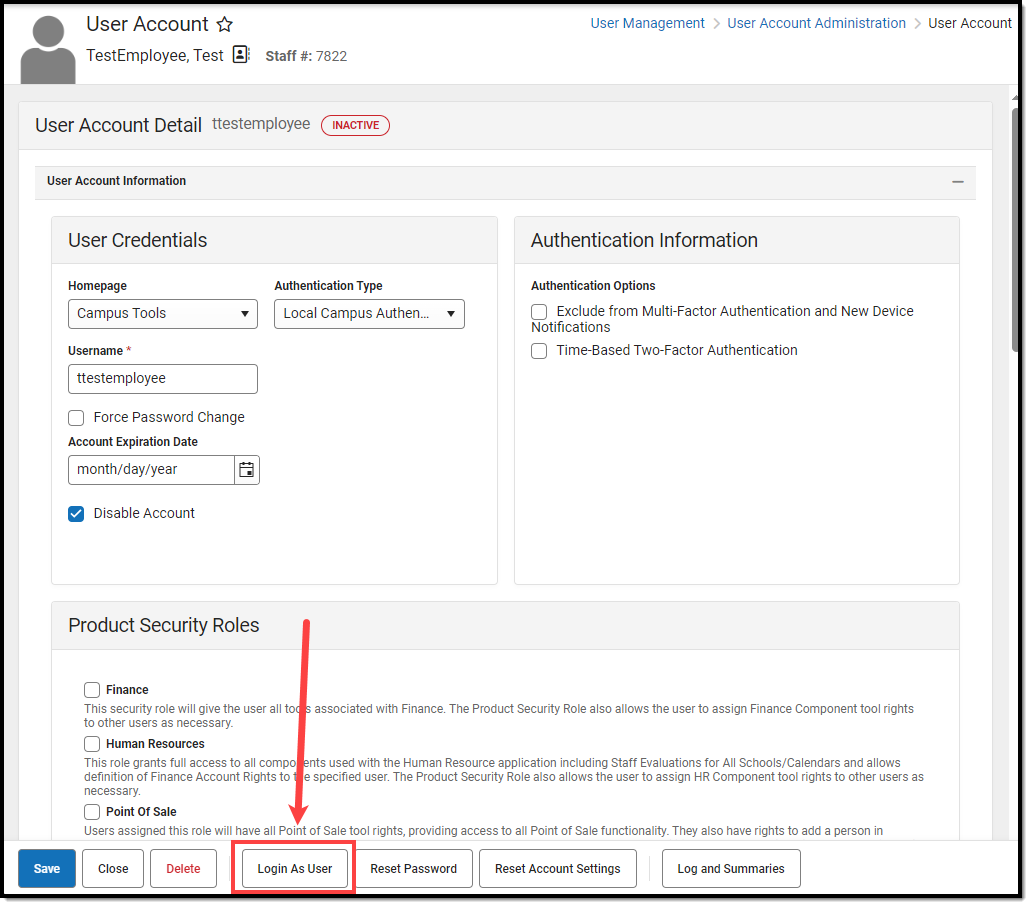
The Login As User button appears only for users with tool rights equivalent to or greater than those of the user they want to log in as, and is available only with the Product Security role. When logging in as another user, they cannot access tools for which they currently do not have tool rights.
This feature is not available to users assigned only to the Student Information System - Group Assignment role.
See the Allowing Non-Product Security Users to Log In as Other Users section for more information on how this feature works for users assigned only to the Student Information System - Login as User role.
The Student Information System - Login As User role is prohibited from logging in as another user with the Student Information System - Login As User role. Users assigned this role may log in as another user only once per Campus session. This behavior was implemented to prevent users from jumping from one user account to another.
The Administrator selecting this button MUST have calendar rights for the school listed on the other user's (the person being logged in) District Assignment page.
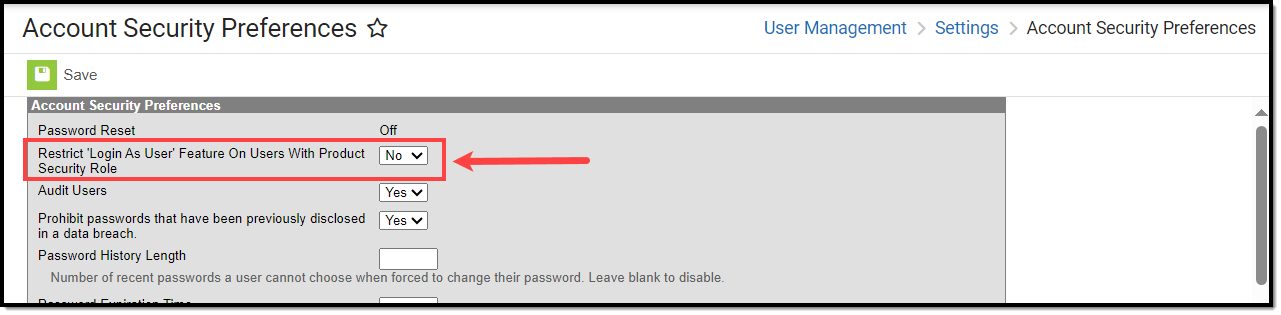
A system preference called Restrict Login As User Feature On Users With Product Security Role controls whether Product Security users may log in as another user with a Product Security role. This preference is found within the Account Security Preferences tool. The default value for this preference is No, which allows Product Security roles to log on as each other.
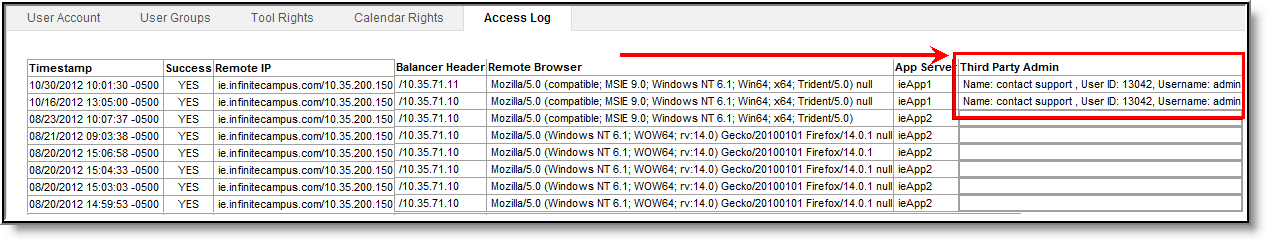
Every Campus login is recorded in the user's Access Log. The Third Party Admin column indicates that another user has used the Login As User button to log into Campus as this user. This column reports the other user's name, user ID, and username.
Allowing Non-Product Security Users to Assign User Groups to Other Users
The Student Information System - Group Assignment security role allows non-security users to assign User Groups to other users without being granted the security and system access provided by other product security roles.
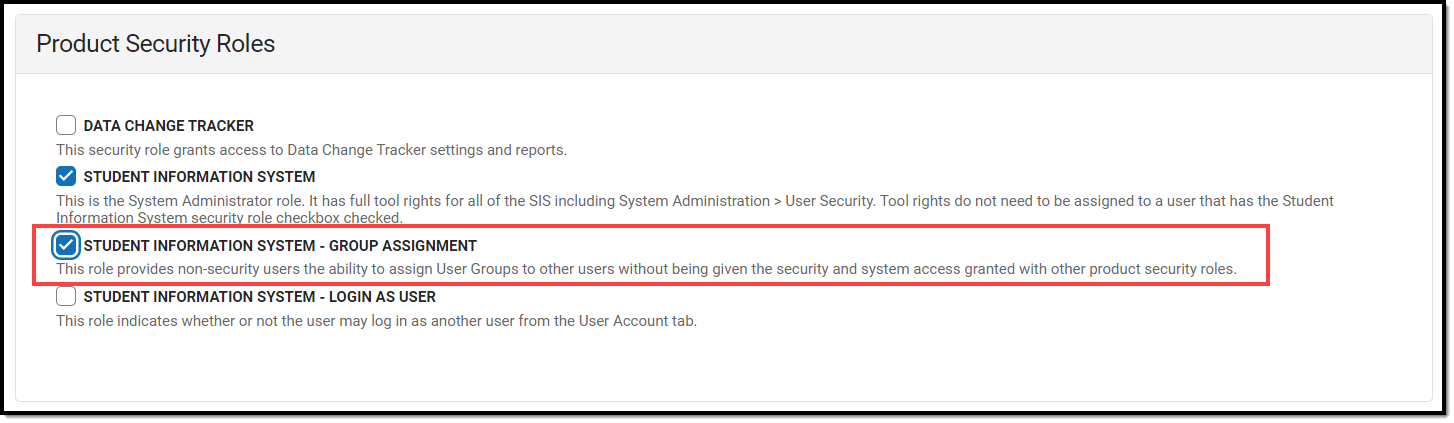
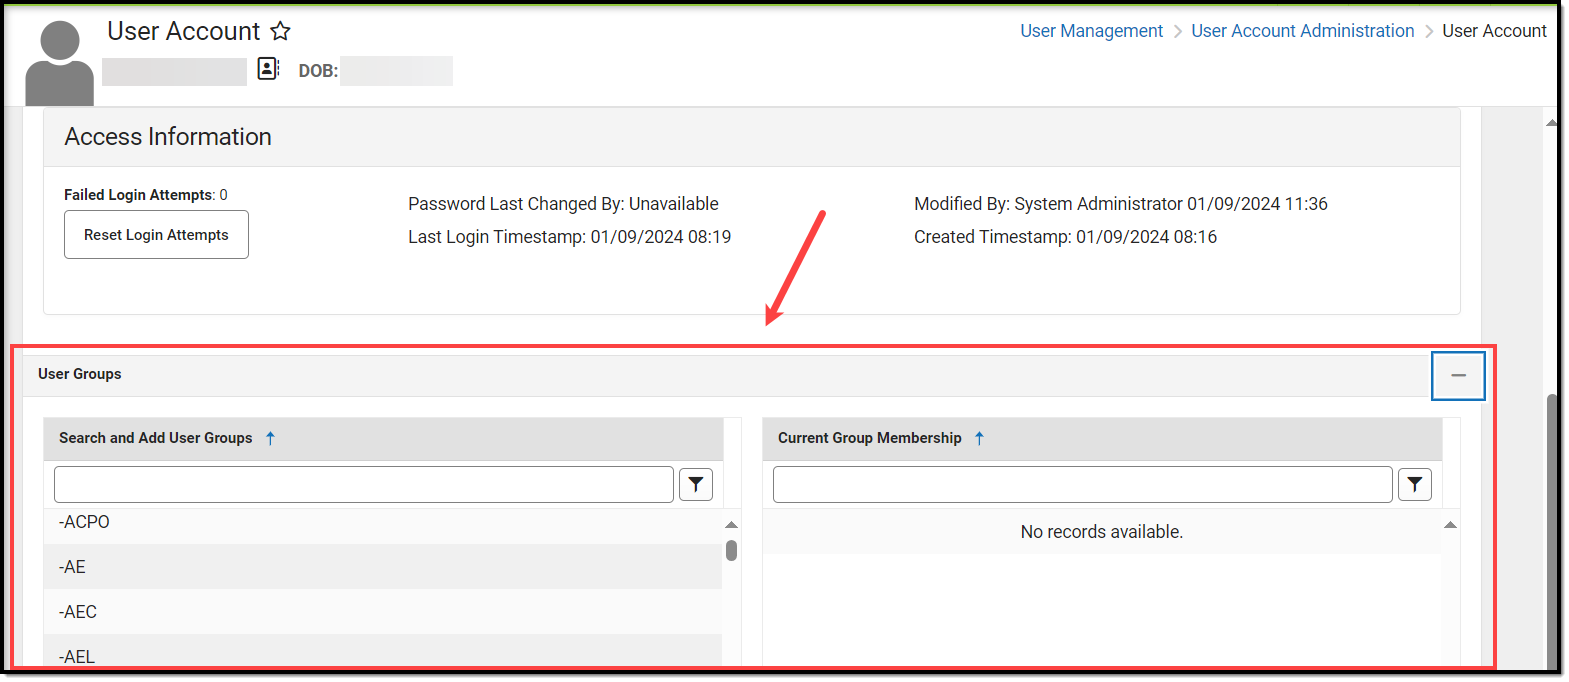
Users assigned this role are allowed to work within Campus to the extent of their tool rights and are granted access only to the User Groups tab within User Security. These users cannot view or modify their own tool rights nor the tool rights of other users.
Allowing Non-Product Security Users to Log In as Other Users
The Student Information System - Login as User security role allows users to access the Login as User feature on the User Account without having the security and system access granted with other product security roles. Users assigned this role are allowed to work within Infinite Campus to the extent of their tool rights and can only log in as other users who have equal to or less than their tool rights.
Users must have at least R (Read) tool rights on the User Account tab to properly log in as other users.
The Student Information System - Login As User role is prohibited from logging in as another user with the Student Information System - Login As User role. Users assigned this role may log in as another user only once per Infinite Campus session. This behavior was implemented to prevent users from jumping from one user account to another.
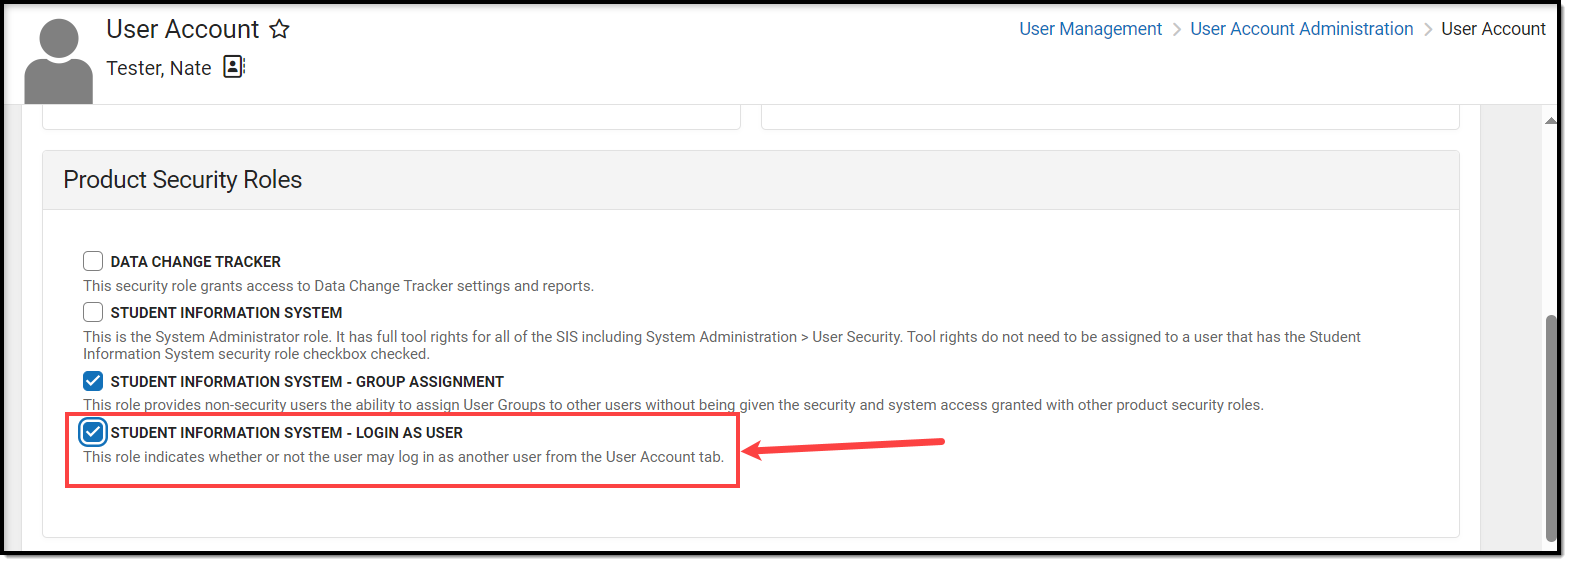
Users assigned this role can log in as another user, but cannot see the other user's tool rights for rights they themselves do not possess. These users can also view or change other users' passwords and usernames only if they have Write tool rights to the User Account. Read tool rights prohibit this role from modifying user account data. This role also prevents users from modifying their own tool rights.
Montana Edition
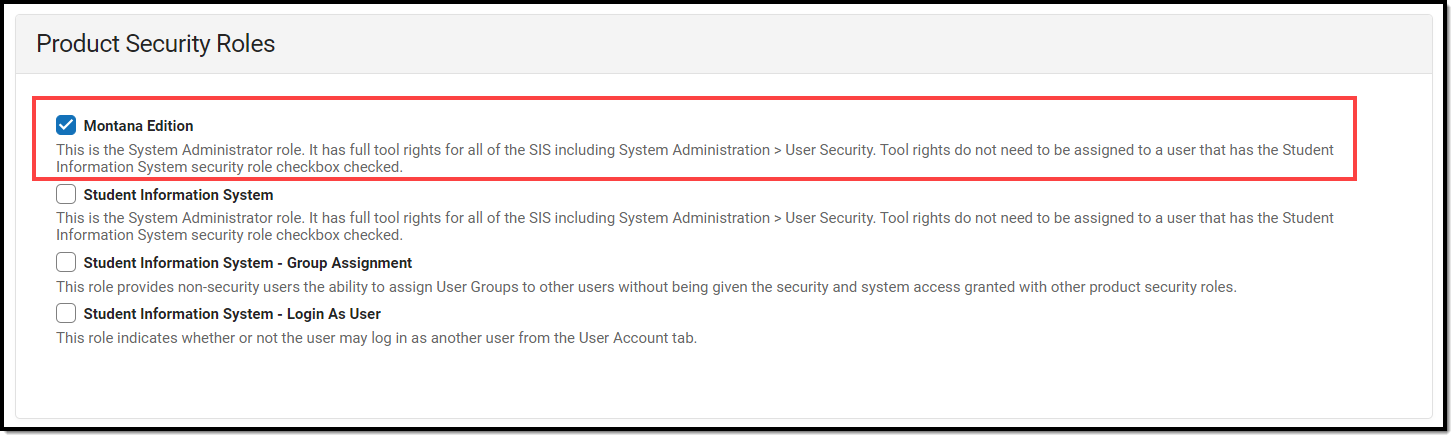
Users within a Montana Edition of Infinite Campus can be assigned the Montana Edition Product Security role. This role grants users full tool rights across the entire SIS, including User Security tools. Users with this role can create and assign security rights, create and assign user groups to other users, and log in as users with tool rights of equal to or less than (via User Account).
Auditing Which Users Are Assigned Product Security Roles
The Product Security Role Report allows you to generate a list of all users (active and disabled) assigned to specific Product Security Roles.